The AI Co-Pilot for
Cyber Risk Leaders
vCDRO — virtual Chief Digital Risk Officer
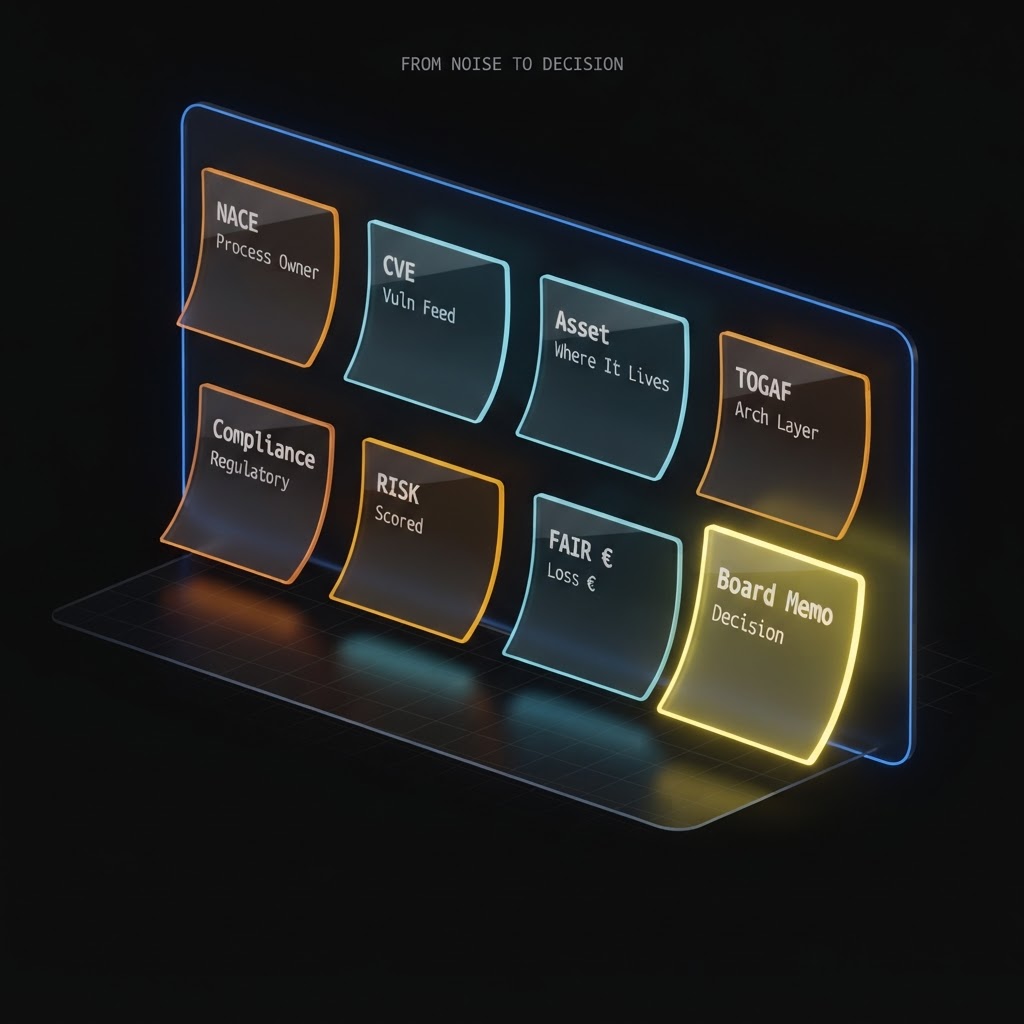
Pieces snap into place autonomously — re-assembled on every scan, no human in the loop.
Why vCDRO is different
Everything connects to this single vCDRO platform.
Autonomous NACE Pipeline
Every vulnerability and asset is automatically linked to European NACE business processes — no manual mapping required.
The value of every layer
From a CVSS score to business risk in euros
Same vulnerability, four lenses. Watch how each vCDRO layer turns an abstract CVE into a decision-grade, owned, quantified business risk — autonomously.
Raw CVSS
Output
10.0
Critical
- Technical severity
- Exploit metrics
- Nothing about your business
Context-free. Where ~95% of the market stops.
The value delta
Every tool you own says "10.0 Critical". vCDRO says it’s a €2.4M risk to your invoicing process — owned, quantified, and ready to route to the person who can fix it.
Autonomous
Re-scored on every new scan, every control change, every framework update — no manual mapping, no spreadsheets, no consultant in the loop.
How vCDRO serves your sector
Every industry has a different risk profile. vCDRO bootstraps from your NACE code to generate a sector-specific risk programme — here’s what that looks like for four common sectors.
Dutch Fintech
DORA + NIS2 for payment institutions
A licensed payment institution under DORA needs continuous ICT risk reporting, third-party concentration mapping, and 24-hour incident notification — all anchored to real business processes.
Healthcare Provider
NEN 7510 + GDPR for hospitals and clinics
A Dutch hospital under NEN 7510 must demonstrate patient data protection across every system — from EHR to medical IoT — with GDPR Article 9 special category data flowing through every process.
Industrial Manufacturing
NIS2 + CRA for critical infrastructure manufacturers
A manufacturer of essential components falls under NIS2 as an essential entity. The Cyber Resilience Act adds product security obligations for any connected device shipped to the EU market.
SaaS / Technology
ISO 27001 + SOC 2 for software companies
A B2B SaaS company needs ISO 27001 for enterprise sales and SOC 2 for US customers. Evidence collection, control testing, and continuous compliance are the bottleneck — not the frameworks themselves.
These are sector capability illustrations, not customer case studies. Each scenario reflects what vCDRO generates during bootstrap for that NACE code.
Continuous Threat Exposure Management
One loop - Five phases - vCDRO at the centre
Armis, Hadrian, Qualys, PassGuard and Horizon3 each do their part. vCDRO turns their signals into one continuous, business-aware exposure programme — the Gartner CTEM loop, running itself.
Phase 1 / 5
Scoping
vCDRO anchors every exposure to your business — NACE processes and TOGAF architecture define what actually matters before a single scan runs.
Suppliers active
Continuous loop
Every new scan re-runs the loop — scoping, discovery, prioritisation, validation and mobilisation happen without a human in the middle.
Regulatory Coverage Matrix
vCDRO covers ~85% of the Dutch Cybersecurity Act (Cbw) and Critical Entities Resilience Act (Wwke) obligations — everything from risk analysis to incident reporting and board accountability.
vCDRO Coverage Matrix
Cbw + Wwke7 of 9 obligations fully covered by vCDRO modules. 2 obligation(s) have external final steps.
Registration Obligation
Data & checklist prepared; actual registration via mijn.ncsc.nl is external
Duty of Care
Risk analysis, vulnerability management, compliance frameworks and asset inventory
Incident Reporting Obligation
IR playbooks, live incident mode, MTTD/MTTR metrics and real-time alerting
Board Accountability
Board memos, governance review and dashboard — training is external
Supervision & Enforcement
Audit trail, evidence locker, governance review and NIS2 dashboard
Critical Entity Risk Analysis
CRR, BIA and FAIR-based quantitative risk analysis
Resilience Measures
Cyber resilience fully covered; physical security is external
Disruption Reporting Obligation
IR hub with live incident mode and lessons learned
Supplier Resilience
Vendor risk management and supply chain compliance controls
vCDRO provides data, checklists and preparation for external processes (NCSC registration, board training, physical Wwke security). The final action takes place outside the platform.
Download our whitepapers
Seven resources that articulate the vCDRO philosophy, the autonomous architecture, the quantified business case, a candid competitive analysis, and the Horizon3 + vCDRO CTEM combination.
White papers
Seven introduction resources that articulate the vCDRO philosophy, the autonomous architecture, the quantified business case, a simple slide deck for SMEs, a detailed external analysis of the 10-stage pipeline, a candid competitive analysis against the broader vCISO market, and a brief on the Horizon3 + vCDRO autonomous CTEM combination. Download as PDF.
Scanner + vCDRO: What It Means for Your SME
A plain-language introduction for SMEs — how vCDRO turns your scanner’s wall of red into prioritised, financially-quantified business decisions. Simple enough to share with non-technical stakeholders.
The vCDRO Approach
A punchy executive brief for boards and decision-makers — why business-first, financially-quantified risk management leaves every existing tool behind.
From Vulnerability Noise to Boardroom Clarity
A deep strategic white paper on the autonomous NACE pipeline, FAIR financial quantification, and the closed-loop architecture that makes vCDRO self-maintaining.
The vCDRO Business Case
A quantified breakdown of time, cost and risk savings by role — from SOC analyst to audit committee — showing exactly what the platform delivers and what it replaces.
The vCDRO Unique Pipeline Approach
An external view on how powerful the vCDRO approach really is — a 10-stage pipeline from CVE ingestion to board report, with core strengths, challenges, and an overall maturity assessment.
How vCDRO Compares to the vCISO Market
A candid competitive analysis — where vCDRO genuinely outperforms compliance automation, enterprise GRC, and consultant vCISO services, and where established competitors still lead.
Autonomous CTEM: Horizon3 + vCDRO
A focused brief on the Horizon3 NodeZero + vCDRO combination — a near-fully-autonomous CTEM programme for organisations that cannot staff a 24/7 SOC.
Pricing that scales with your organisation
Transparent per-month pricing based on organisation size. Every tier includes the autonomous NACE pipeline and AI co-pilot.
Starter
Essential
Up to 25 employees
- Security Posture Dashboard
- Asset Inventory
- Vulnerability Management
- NACE Business Intelligence
- Patch Prioritisation
Growth
Growing
26 – 50 employees
- Everything in Starter
- Compliance Hub (all frameworks)
- Board Reports
Scale
Scaling
51 – 100 employees
- Everything in Growth
- IR Hub
- Human Risk Hub
- Business Impact Analysis
- Vendor Risk Management
Professional
Professional
101 – 250 employees
- Everything in Scale
- FAIR Risk Quantification
- Full Resilience Hub (CRR, BCM, Gap Tracking, Strategic Mapping)
- TOGAF Architecture View
- Financial Risk Modelling
Enterprise
Enterprise
251 – 2,000+ employees
- Everything in Professional
- Dedicated vCDRO Advisor
- Custom NACE Integrations
- Tabletop Exercises
- SLA Guarantee
All prices in EUR · Annual billing available · MSSP white-label options on request
Contact Us
Reach out to our team — we’re happy to answer your questions about vCDRO and NetBoss services.
Our Office
Our offices are located at the following addresses:
Websites
Visit our websites for more information about our services and security insights: